 By Suro Senen
By Christina Newberry
Published by Strategy News Desk
Main Facts: The Escalating Threat Landscape
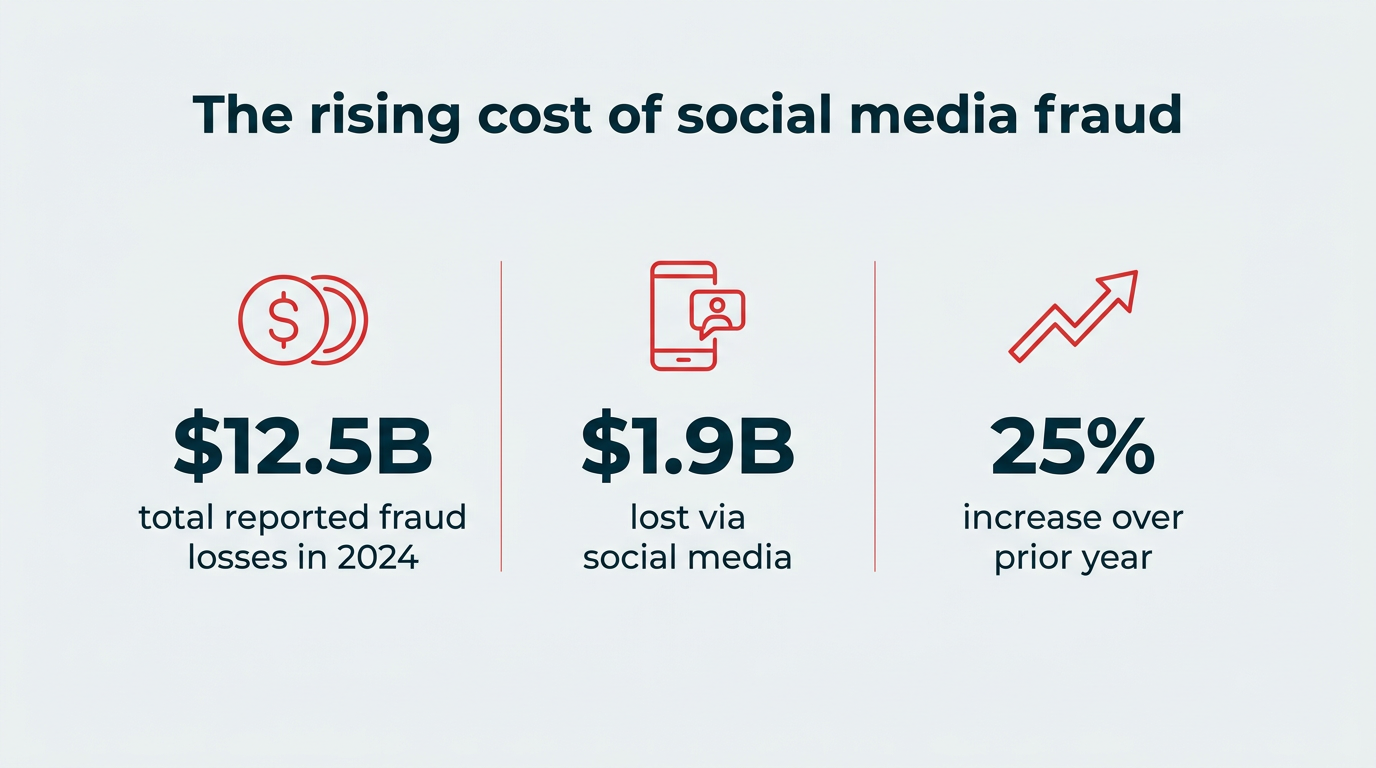
As social media platforms cement their positions as essential hubs for global communication, brand marketing, and direct customer service, they have simultaneously become prime targets for highly sophisticated cybercriminals. According to recent data from the Federal Trade Commission (FTC), consumers reported an alarming $12.5 billion in total fraud losses in 2024, representing a staggering 25% surge over the previous year. Of those reported figures, social media accounted for $1.9 billion in direct losses, establishing it as the single most lucrative channel for digital fraudsters.

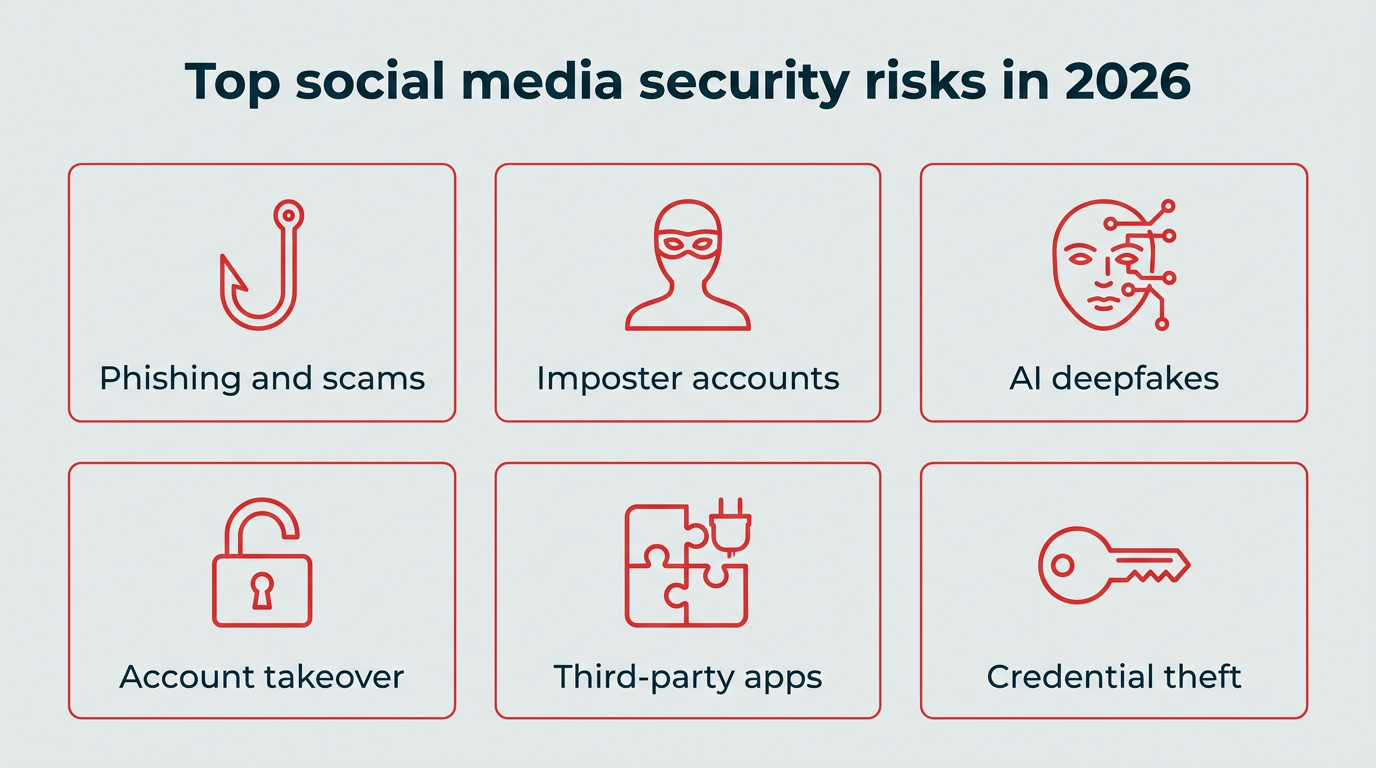
Today, social media security is no longer merely a passive IT precaution or a marketing afterthought; it is an urgent enterprise risk management imperative. The threat vector has transformed dramatically. Opportunistic scammers and manual phishing attempts have been largely superseded by organized, automated syndicates leveraging artificial intelligence, deepfake technology, and advanced malware campaigns. For businesses operating on platforms like Instagram, LinkedIn, Facebook, and X (formerly Twitter), a single compromised account can instantly destroy consumer trust, drain advertising budgets, and expose sensitive proprietary or customer data within hours.
Chronology of Evolution: From Simple Phishing to Autonomous AI Attacks
To understand how organizations must defend themselves in 2026, it is vital to trace how social media vulnerabilities have evolved over the past decade:

- The Early Era (Pre-2015): Security threats on social media were largely confined to primitive spam, basic credential harvesting via fake login pages, and occasional direct-message malware links.
- The Rise of Imposter Accounts (2015–2020): As brands built massive digital followings, fraudsters recognized the value of brand impersonation. Cybercriminals began deploying lookalike profiles to trick consumers and harvest corporate credentials, prompting major networks to introduce verification programs.
- The Social Engineering Boom (2020–2023): Attackers shifted their focus toward human error. Employees were frequently targeted with spear-phishing campaigns designed to steal administrative passwords, leading to high-profile account takeovers (ATOs) that disrupted public markets and corporate reputations.
- The AI and Deepfake Era (2024–Present): Artificial intelligence automated social engineering. Today’s threat actors deploy deepfake audio and video to impersonate corporate executives, launch automated spear-phishing campaigns at scale, and utilize generative AI chatbots to legitimize fraudulent customer support channels.
Supporting Data and Statistical Insights
Recent reports from leading cybersecurity and regulatory bodies highlight the severe quantitative risk facing organizations on social media:
- $12.5 Billion: Total reported fraud losses in the United States in 2024 (FTC).
- $1.9 Billion: Total losses attributed specifically to social media scams, making it the top contact method for fraud targeted at working-age adults.
- 62% of Organizations: Enterprises that experienced at least one deepfake attack over the past year, according to a recent Gartner survey. Notable incidents include a corporate finance employee in Hong Kong transferring $25 million during a video call where all other participants were sophisticated deepfakes of senior colleagues.
- 22% of Breaches: Security incidents involving stolen credentials, as highlighted in Verizon’s Data Breach Investigations Report, emphasizing how reused passwords allow attackers to cascade across systems once a single social account is breached.
- Tens of Millions of Fake Accounts: The scale of automated defense mechanisms deployed by major tech platforms. For example, LinkedIn’s Community Report revealed that automated systems proactively block 97.8% of fake accounts at registration, with another 99.7% stopped before member reports—leaving only a fraction to slip through the cracks.
Official Responses and Industry Standards
In response to the escalating crisis, regulatory bodies, platform operators, and enterprise software providers have issued rigorous guidelines and compliance frameworks.
Government agencies and financial regulators are increasingly holding organizations legally accountable for negligence in customer data protection and brand impersonation monitoring. In regulated sectors such as finance, healthcare, and the public sector, maintaining a verifiable audit trail of social media publishing and communication is no longer optional—it is a regulatory mandate.
Platform operators, including Meta, LinkedIn, and X, have heavily invested in automated threat mitigation, deploying machine learning models to intercept fraudulent activity at the point of registration. However, tech platforms consistently emphasize that platform-side defenses cannot fully protect corporate assets. Organizations must implement robust internal access controls, multi-factor authentication (MFA), and passkey integrations to secure their digital perimeters.
Furthermore, security leaders advocate for comprehensive risk-management integration. Platforms that offer FedRAMP authorization, Cyber Essentials compliance, and third-party monitoring capabilities—such as Hootsuite Social OS, ZeroFOX, and 1Password Business—have become gold standards for enterprise-grade social media governance.
Implications: The 2026 Social Media Security Checklist
Mitigating modern social media threats requires a proactive, multi-layered defense strategy. Organizations must adopt the following eight core practices to harden their security posture:

1. Implement Strong Passwords and Enterprise Password Managers
Every social media account must be secured with a long, randomly generated, and completely unique password. Relying on employee memory or unsecured spreadsheets is a recipe for disaster. Using enterprise tools like 1Password Business ensures that shared vaults remain secure, credentials are automatically monitored for known breaches, and departing employees can have their access revoked instantly.
2. Enforce Passkeys and Two-Factor Authentication (MFA)
Multi-factor authentication is a non-negotiable baseline. However, where supported, passkeys represent the superior security standard. By replacing traditional passwords with cryptographic credentials tied directly to an approved device, passkeys render traditional phishing pages obsolete because there are no text-based credentials for attackers to steal.

3. Apply Role-Based Access and the Principle of Least Privilege
Do not share raw account credentials across entire marketing or customer service teams. Apply the principle of least privilege: grant employees only the narrowest access required to perform their specific duties. Platforms like Hootsuite allow teams to collaborate, schedule, and publish content through structured approval workflows without ever exposing the underlying platform passwords.
4. Conduct Comprehensive Employee Training
Because human error remains the primary vector for cyberattacks, security awareness training must be continuous. Organizations should fold social media threat awareness into onboarding programs and conduct refreshers at least twice a year. Employees must be trained to recognize AI-generated phishing messages, suspicious direct messages, and social engineering traps.

5. Deploy Real-Time Monitoring and Social Listening
Waiting for a customer to report a fake account or fraudulent coupon campaign is far too late. Enterprises must utilize real-time social monitoring and listening applications (such as Hootsuite’s Lumen or ZeroFOX) to track brand mentions, spot unusual sentiment swings, and instantly identify imposter accounts before they cause reputational or financial harm.
6. Regularly Audit Privacy Settings and Connected Apps
Third-party applications pose a silent threat to social media security. Apps promising automated follower growth or analytics often demand expansive account permissions. Security teams must audit connected third-party apps and revoke access for unused or unrecognized integrations on a strict quarterly basis.

7. Secure Mobile Devices and Endpoints
Because a vast majority of social media publishing and monitoring occurs on mobile devices, endpoint security is directly tied to social media security. Organizations must mandate screen locks, enforce automatic software updates, enable remote-wipe capabilities, and require virtual private networks (VPNs) when accessing corporate social accounts over public Wi-Fi networks.
8. Institutionalize Quarterly Audits and Incident Response Plans
Security threats evolve daily. Organizations must establish a formal schedule for quarterly security audits—reviewing access permissions, validating MFA status, updating privacy settings, and testing incident response protocols.
Summary Reference Table: Enterprise Security Matrix
| Security Action | Frequency | Responsible Team |
|---|---|---|
| Confirm 2FA or passkeys on all accounts | Monthly | Social Media Team |
| Review access permissions and publishing rights | Quarterly | Social Media Lead & IT |
| Audit and revoke connected third-party apps | Quarterly | IT Security |
| Check platform privacy and security settings | Quarterly | Social Media Team |
| Monitor for imposter accounts and brand mentions | Daily | Social Media Team |
| Rotate passwords after staff or role changes | As Needed | Social Media Lead |
| Conduct phishing and social engineering training | Twice Yearly | IT Security & HR |
| Review and update social media security policies | Quarterly | Social, IT, & Legal |
| Test the incident response plan | Annually | Social, IT, & Communications |
| Verify device locks, updates, and VPN usage | Quarterly | IT Security |
By institutionalizing these controls, maintaining rigorous oversight, and combining governed publishing platforms with external threat intelligence, organizations can successfully navigate the treacherous waters of the 2026 threat landscape, protecting their brands, their customers, and their bottom lines.
 Raul Delapena Setiawan
 Evan Lee Salim
